See the credentials your companyhas already leakedout there
Over billion stolen credentials indexed. Type your domain and see right now what is exposed about your company.
off your first purchase
Ends in –d ––:––:––Trusted by
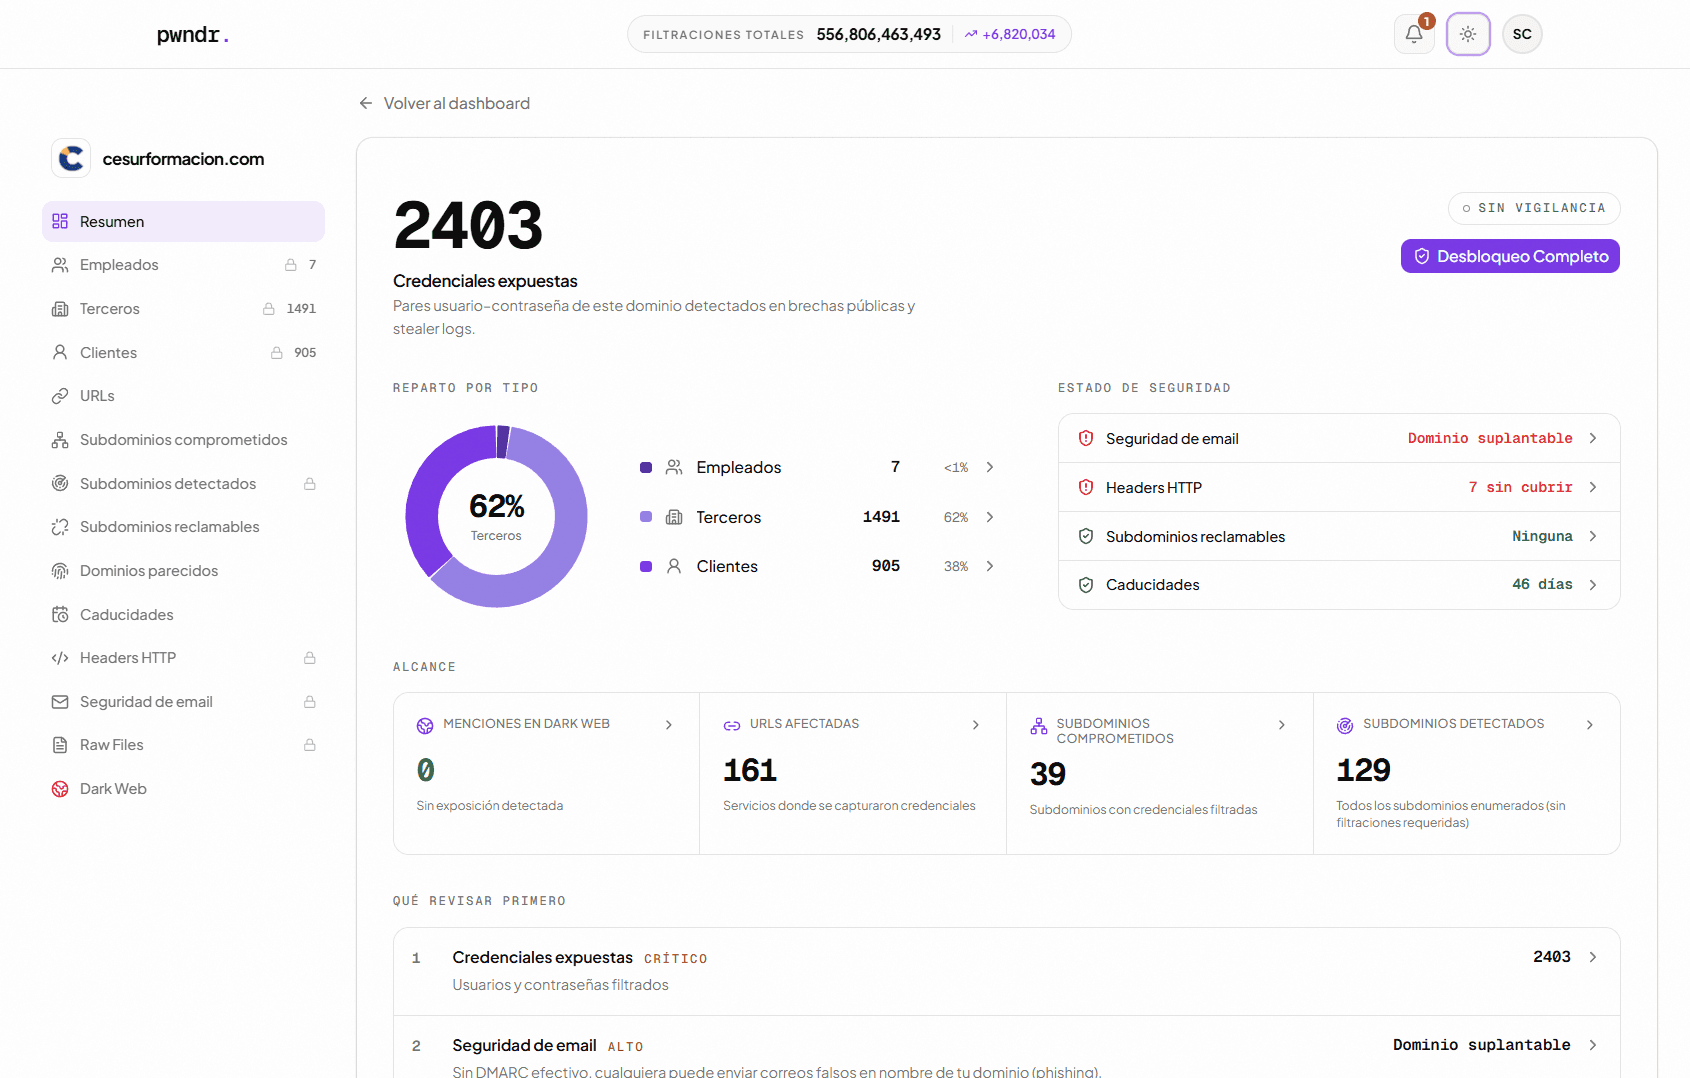
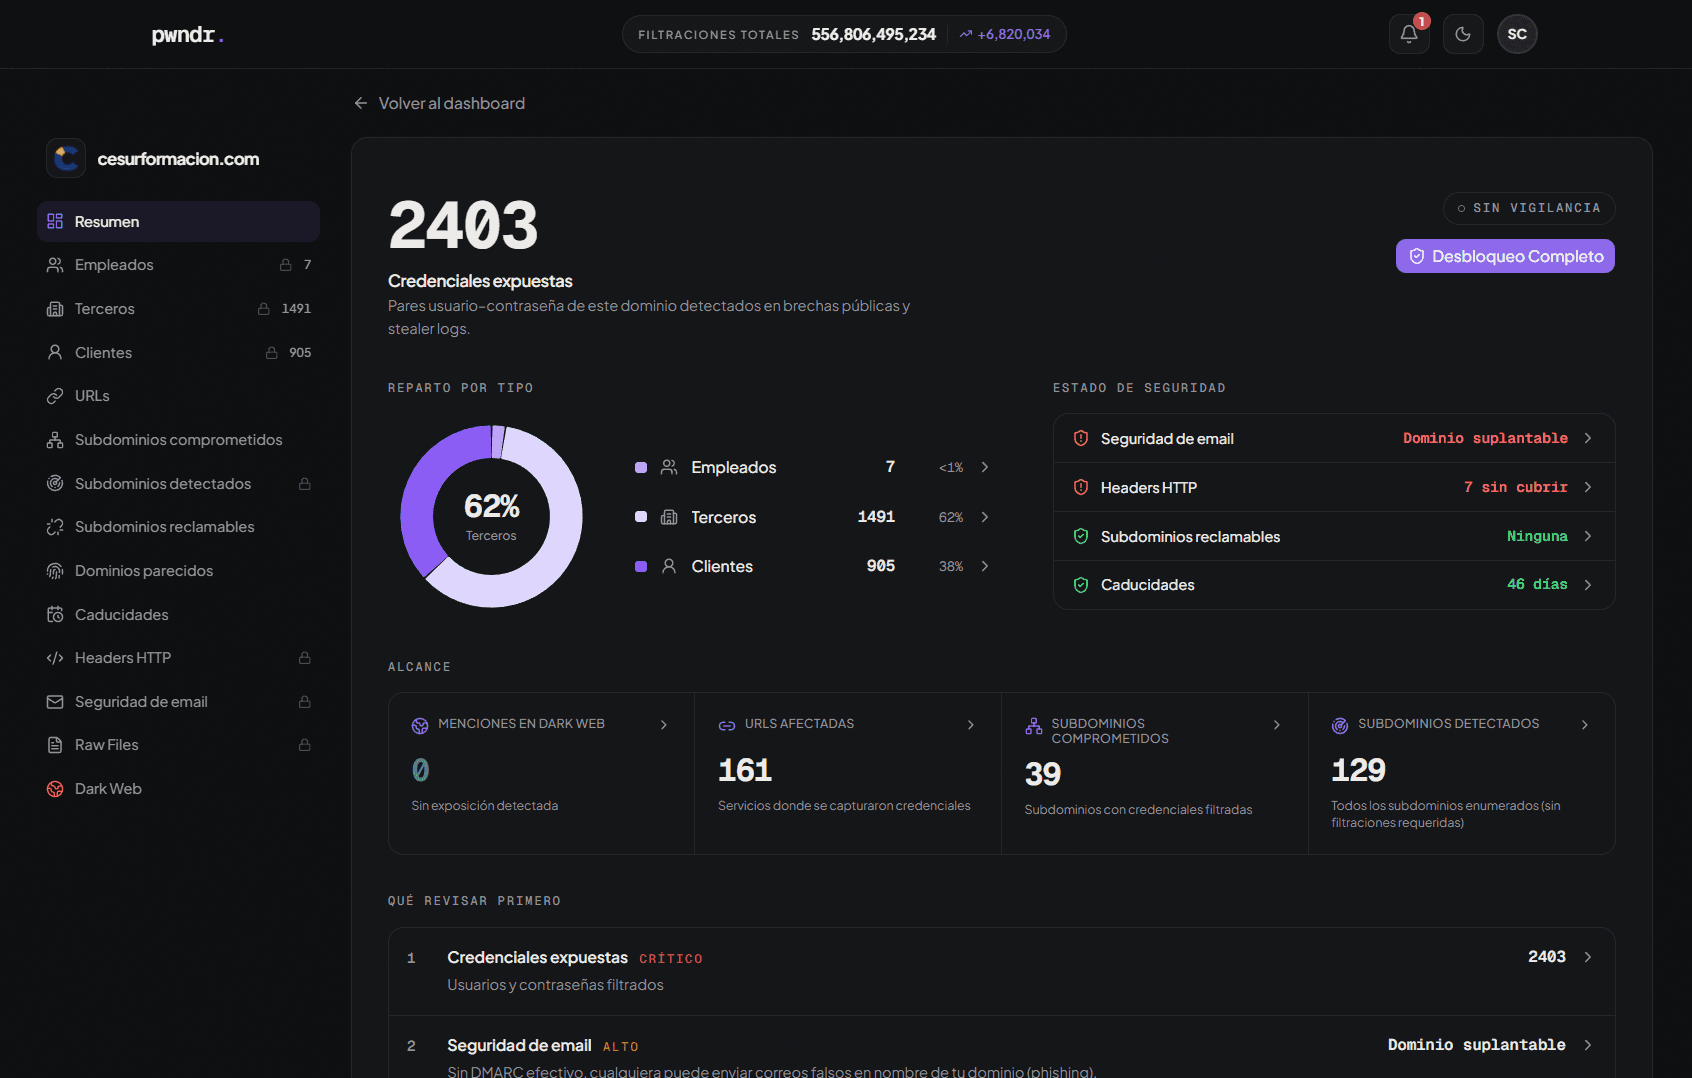
What we find when we scan your domain
Your team's passwords, stolen by infostealers and put up for sale on forums, Telegram and dark web markets.
The accounts of the people using your applications. One reused credential of theirs is an open session in your product.
Partners with access to your systems. This year's attacks on Inditex and Endesa came in through exactly that door.
Everything hanging off your domain: the compromised ones, the ones we merely detected, and the ones someone could claim.
SPF, DMARC and MX checked one by one. If anyone can send mail pretending to be you, you'll see it here.
Registrations that swap a single character of yours to fool your customers — and your own people.
We sweep hacker forums, Telegram channels and illicit markets to see whether anyone is naming your domain.
Hover over or tap each one to see the detail.
The platform that watches it, audits it and alerts you
Dark Web Monitoring
Forums, Telegram and illicit markets, tracked 24/7.
Exposed Subdomains
We enumerate your entire Shadow IT and flag which subdomains have leaked credentials.


Connect it to your AI
Query your leaks from Claude, ChatGPT or Gemini over MCP, without leaving the chat.
Reports & Export
Executive report as PDF or every credential as CSV, with no download limits.
HTTP & Email Audit
SPF, DMARC and security headers: detect if your domain can be spoofed for phishing.
Instant Alerts
Email alerts in under 60 seconds, the moment a new breach appears.
What are you waiting for?
Check for free if your company is exposed. One search instantly cross-checks leaked credentials, dark web mentions and exposed subdomains. No signup.
The questions that always come up
Seeing your own company's leaked credentials raises fair questions. These are the ones we get every week, answered straight.
Still have a question?
Talk to us01Is this legal?
Yes, completely legal. pwndr indexes information that has already been published by cybercriminals in underground forums, Telegram channels and paste sites. We don't access any private systems or perform offensive actions. Pure defensive intelligence.
02How does pwndr obtain leaked credentials?
We continuously monitor over 40 sources: dark web forums, stealer logs, cybercrime Telegram channels and paste sites. We process millions of records per hour and cross-reference them with the domain you query.
03What does the full unlock include?
Full access to the list of leaked credentials for that domain: emails or usernames, plaintext passwords, source URL and breach date. Plus real-time email alerts when new breaches appear, dark web search and unlimited CSV downloads. Cancel anytime.
04Who is pwndr for?
For anyone who wants to know if their credentials or their organization's are exposed: individuals, freelancers, IT managers and companies of any size. No technical knowledge required.
05Is my data safe with pwndr?
We only store the queried domain and the data needed to manage your account and payment. We don't sell or share information with third parties. GDPR compliant.